
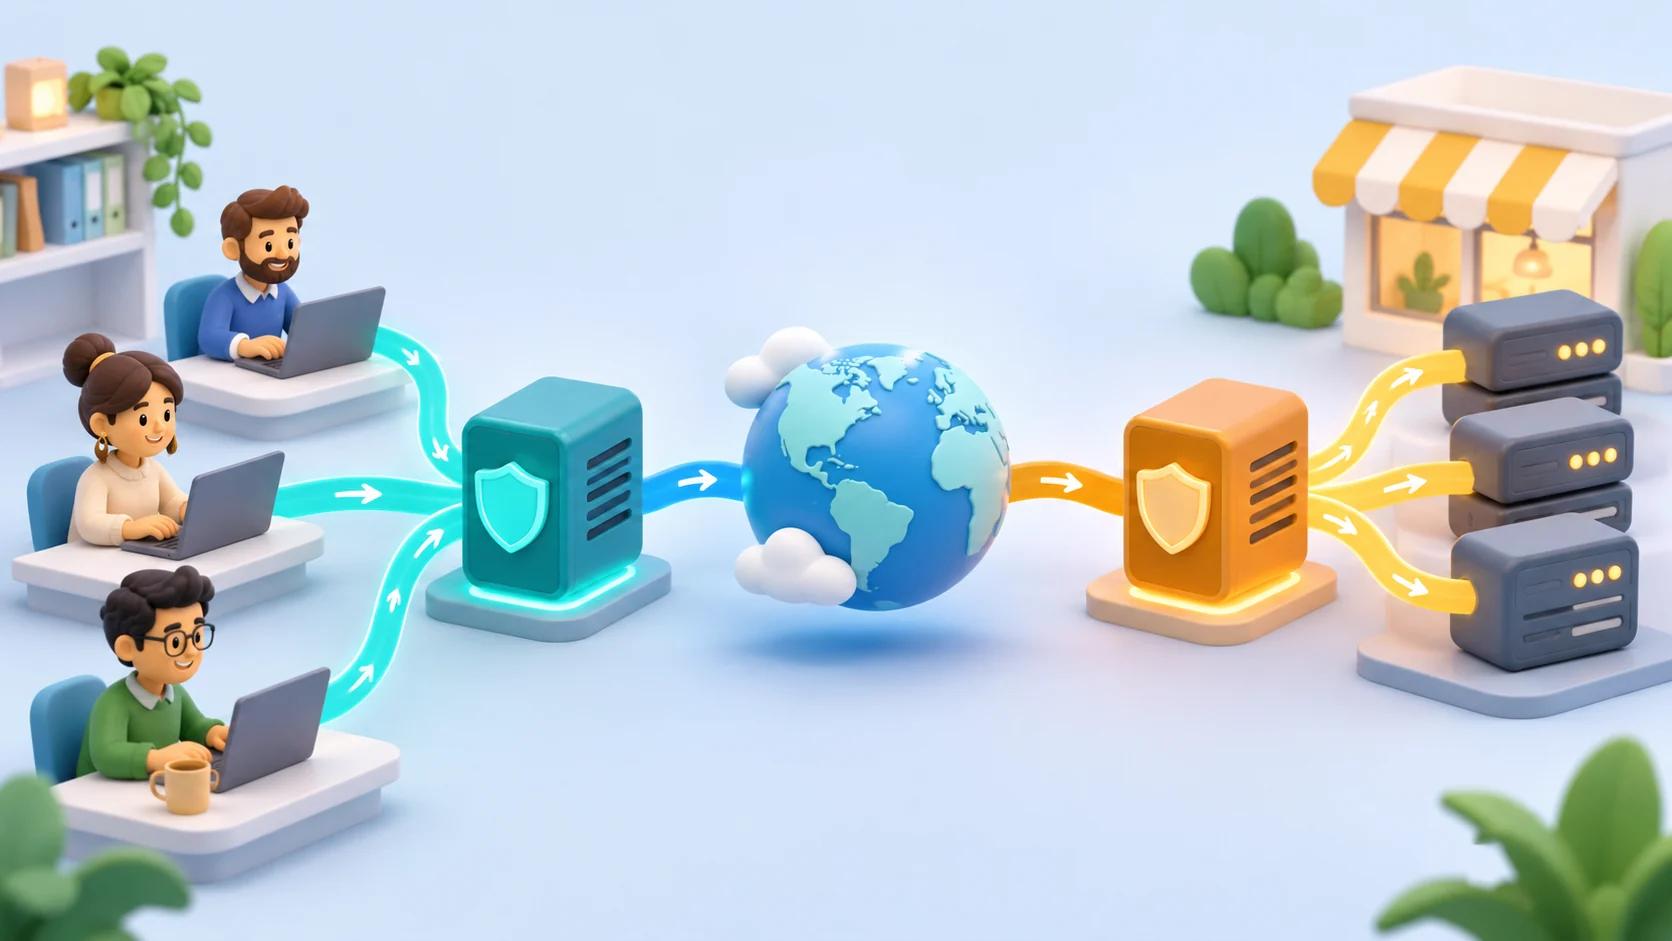
A forward proxy acts on behalf of clients making outbound requests. A reverse proxy acts on behalf of servers receiving inbound requests. In a forward proxy vs reverse proxy decision, start by identifying whose traffic you want to control: the person or application making a request, or the website receiving it.
Both are intermediaries, and both can send requests onward. Their names describe their role in the architecture, not a promise about security, anonymity or performance. A website gateway does not automatically become an outbound browsing service, and purchasing an outbound proxy does not publish your application to visitors.
TL;DR
- Use a forward proxy when a client needs a defined outbound route or access policy.
- Use a reverse proxy when visitors need an entry point to applications you operate.
- Authentication, encryption, caching and logging depend on the actual configuration, not just the proxy label.
- Both roles can exist in one system, but they have separate owners, credentials and failure modes.
- A residential, ISP or datacenter label describes a network offering; it does not replace the forward-versus-reverse distinction.
The Difference in One Table
| Question | Forward proxy | Reverse proxy |
|---|---|---|
| Who is it acting for? | A client or group of clients | A server or group of servers |
| Typical request path | Application → proxy → destination | Visitor → proxy → application |
| Who usually selects it? | Client operator or network administrator | Website or service operator |
| What is the immediate goal? | Control or route outbound access | Receive and route inbound access |
| Typical authentication concern | May this client use the proxy? | May this visitor access this application? |
| Common operational concern | Endpoint access, credentials and outbound policy | Upstream health, routing, certificates and origin access |
| What does it not automatically provide? | A public entry point for your own website | A different outbound identity for unrelated browser traffic |
These are typical roles rather than restrictions on a particular software package. A capable gateway can support several functions, but each function still needs an explicit configuration. The MDN overview of proxy servers distinguishes forwarding intermediaries and gateways in the HTTP request path.
How a Forward Proxy Works
Imagine a reporting application making an authorized request to an external service. Instead of connecting directly, it sends the request through a configured forward proxy. The proxy establishes the next connection and returns the response through the same logical path.
The client operator may want centralized outbound policy, a controlled network route, or a supported way for an application to reach a destination. The exact result depends on the protocol, the client’s proxy support and the provider’s configuration. Some applications have their own proxy settings; others inherit system or environment settings.
The important operational question is whether the intended application actually uses the proxy. Changing a setting in one tool does not prove that every process on the computer follows it. A background service, browser and command-line client can have different effective configurations.
A forward proxy also does not guarantee that the destination sees no other identifying information. Requests may include account credentials, cookies and application data. Select a route for a legitimate technical need, and evaluate data handling separately from the address used for the network connection.
Example: A Scheduled Data Integration
Consider a hypothetical integration that retrieves permitted supplier data every morning. Its operator wants requests to leave through a documented endpoint. The operator configures the integration’s HTTP client, stores the proxy credential separately from the supplier API token, and checks both route and application behavior.
The proxy credential answers whether the integration can use the intermediary. The supplier token answers whether it can read the supplier’s data. A working proxy does not grant the second permission. Keeping these responsibilities separate makes authentication failures much easier to diagnose.
How a Reverse Proxy Works
Now imagine a public website with an application running on a private service port. Visitors connect to the website’s front door. A reverse proxy receives that traffic and forwards it to the configured upstream application, then returns the application’s response.
The website operator chooses the upstream and controls the entry point. Depending on the design, the reverse proxy may handle TLS termination, routing between services, buffering or load distribution. Those are configured capabilities, not features to assume every deployment includes.
The NGINX reverse proxy documentation explains passing requests to an upstream with proxy_pass, setting request headers and controlling buffering. This guide focuses on choosing the role; installation and directive details belong to the documentation for the software you actually deploy.
A reverse proxy cannot make an unhealthy application healthy. If the upstream database is unavailable, putting another component in front of it does not restore the missing data. It can provide a controlled failure response or route to another healthy instance only when the architecture has been designed to do so.
Example: Two Internal Applications Under One Domain
Suppose a small team operates a dashboard and a documentation service. This is a hypothetical design, not a benchmark. A reverse proxy can provide a defined public entry point and send requests to the appropriate application according to configured hosts or paths.
The team still needs to decide who can access each application, how certificates renew, and whether the origin services are reachable directly. A neat domain structure is useful, but it does not replace access control. Test both the expected public route and any unintended alternate entry points.
Authentication and Trust Are Different on Each Side
A forward proxy may require a username and password before forwarding traffic. The application can also need its own destination credentials. Keep the two identities separate in configuration, logs and incident reports.
With a reverse proxy, visitors may authenticate to the application or to an access layer in front of it. The application must understand which headers or identity assertions it can trust. Accepting a visitor-supplied identity header without a trusted boundary can undermine the intended control.
For example, an application may want to record the original visitor address after traffic passes through a gateway. That requires a deliberate trusted-proxy configuration. Merely reading a forwarded header does not establish that its contents are authoritative. The application and gateway settings need to agree on which components are allowed to supply it.
In either design, define who can change the routing configuration. A proxy administrator can affect where requests go and what information passes through the intermediary. Treat that authority as a meaningful operational permission, not a harmless convenience setting.
Does Either Proxy Automatically Encrypt Everything?
No. Identify the connections separately. There may be a connection from client to proxy and another from proxy to destination or upstream. Encryption on one connection does not establish encryption on the other.
For a reverse proxy that terminates HTTPS, decide whether the connection to the application also requires TLS, and verify the relevant certificate and trust settings. For a forward proxy, distinguish the destination URL from the protocol used to reach the proxy endpoint.
Write those choices down in the architecture record. Avoid a diagram that labels the whole route “secure” without explaining where encryption begins and ends. The useful review asks what each intermediary can observe, where credentials travel, and which party manages the trust configuration.
A Practical Selection Process
1. Write the Request in Plain Language
Use a sentence such as “our worker calls an external API” or “customers open our dashboard.” Name the requester and the destination. This small exercise usually identifies the relevant side of the proxy distinction before any product comparison begins.
If the requirement says only “we need a proxy,” ask what must change: outbound routing, inbound application access, authentication, or traffic management. Those goals can require different components.
2. Identify the Boundary You Control
List the client, the intermediary and the destination. Mark which systems your team operates and which belong to another organization. Do not design a solution that assumes administrative control over a third-party website.
For an application you own, you can choose an inbound gateway and configure the origin. For a third-party API, you control your client and its authorized route, but the API’s account permissions and usage rules remain outside that boundary.
3. Define the Required Protocols and Behavior
Include the application protocol, authentication method, request size, streaming behavior and expected connection duration. A successful short page request does not prove that long-lived streams or large uploads will behave correctly.
Use representative authorized tests, and record the client version. Avoid treating the word “proxy” as evidence that every protocol or authentication mechanism will work. Compatibility is a property of the complete connection path.
4. Assign an Owner to Each Failure
Decide who checks client configuration, proxy availability, application health and certificate renewal. Give support staff enough sanitized information to distinguish a proxy authentication failure from an upstream application failure.
Also decide how to disable or roll back a routing change. A reversible configuration is much easier to operate than an undocumented dependency that everyone discovers during an outage.
5. Verify the Actual Result
For a forward proxy, test that the intended application follows the selected route and completes its real task. For a reverse proxy, test the public hostname, routing, authentication and expected upstream behavior. Check that unintended direct access is restricted where your design requires it.
Keep the result as a small acceptance record rather than a screenshot of one successful request. Include normal behavior, one controlled failure, and the recovery step. This creates a reference for future changes.
Can a System Use Both?
Yes. A web application may receive visitors through a reverse proxy while its background worker uses a forward proxy for an authorized external integration. These are separate request paths, even when the components run in the same infrastructure.
Keep their credentials, logs and configuration names distinct. “Proxy password” is an ambiguous secret label when a deployment contains several intermediaries. Prefer names that identify the service and purpose without revealing the secret itself.
Also consider failure independence. If the outbound proxy is unavailable, should the public application remain available while scheduled integrations pause? If the inbound gateway fails, can operators still reach a recovery console? These questions reveal whether one component has accidentally become a dependency for unrelated work.
Where Hosting and Proxy Products Fit
A server gives you a place to run software. A forwarding service gives a compatible client a route for requests. They can be combined, but neither automatically includes the other. The existing VPS versus residential proxy comparison expands that distinction.
For hosting an application or gateway, evaluate the runtime and maintenance responsibilities of Cloud VPS. If you choose NGINX Proxy Manager, the existing NGINX Proxy Manager deployment guide covers that separate installation task. The broader VPS management guide is relevant to keeping the underlying server maintained.
An outbound proxy’s ISP or datacenter classification is a different decision. It does not tell you whether your website needs a reverse proxy, and it does not remove the need to configure authentication and application access. Choose the architecture first, then assess the network offering against a specific requirement.
FAQ
What Is the Main Forward Proxy vs Reverse Proxy Difference?
A forward proxy serves clients making outbound requests; a reverse proxy serves applications receiving inbound requests. Identify which side you operate and what traffic behavior you want to change before selecting software or a service.
Can a Reverse Proxy Change My Browser’s Outbound IP?
Not simply by existing in front of your website. It handles requests addressed to the applications it serves. Routing unrelated browser traffic through an intermediary requires a separate supported forward-proxy or network configuration.
Is a Reverse Proxy the Same as a Load Balancer?
No. Load balancing is one possible function of a reverse-proxy design. A reverse proxy can forward to a single upstream, and a load-balancing system can operate in different ways. Inspect the actual configuration instead of assuming redundancy from the label.
Does a Forward Proxy Make Requests Anonymous?
No such guarantee follows from the role. Account logins, cookies, request data and operator logs still matter. Evaluate what information is sent and retained, and use the service only for access you are authorized to perform.
Do I Need Both for a Small Website?
Not necessarily. Start with the application’s requirements. A managed hosting service may already handle the inbound entry point, and ordinary outbound requests may need no extra proxy. Add a component only when it solves a documented requirement and someone can maintain it.
Is a Transparent Proxy a Third Direction?
No. Transparency describes how interception or client awareness works in a particular context; it is a separate dimension from whose requests the intermediary serves. Use precise descriptions of the traffic path rather than treating every proxy label as a competing architecture.